Automated Software Bill of Materials (SBOM) Management
Generate SPDX and CycloneDX SBOMs from every scan, keep them current as dependencies change, and enrich them with the risk data auditors and customers ask for.
Challenges
Software development is dynamic. Manual SBOMs aren’t.
With different teams using different tools and a constant stream of updated open source packages, an accurate SBOM is hard to maintain by hand.

Constant change
Identifying every open source dependency and monitoring each for updates overwhelms most security teams.
Manual processes
Tracking changing components and versions by hand almost guarantees human error and a stale document when a customer or regulator asks for it.
The risks of bad automation
While automation is crucial to success, companies face increased risk if it isn’t done right.
Opportunities
Beyond static to effective
Using SBOMs to meet compliance or customer requirements is the starting point. An SBOM that updates itself and carries risk context becomes the working inventory your security program runs on.

Cut the risk of human error
Effective automation that automatically updates open source dependencies and packages across all applications eliminates error-prone manual processes.
Accurate risk assessment
Automated dependency identification delivers up-to-date risk assessments and ensures license compliance.
Prioritize high-risk vulnerabilities
Not every vulnerability poses a risk. By knowing whether your code reaches a vulnerable function, you can prioritize remediation based on actual exposure.
The solution
Every scan produces a current SBOM
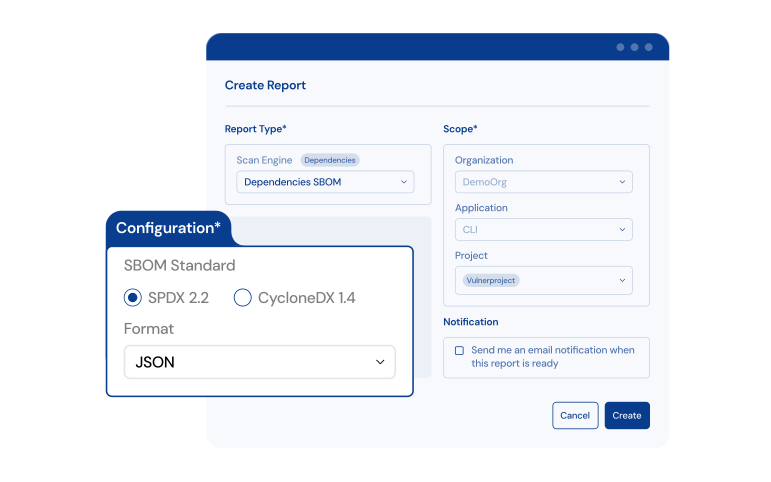
Mend SCA automatically generates accurate, comprehensive SBOMs in both SPDX and CycloneDX formats. It incorporates VEX data and integrates third-party SBOMs — so your software stays secure, compliant, and transparent to every downstream consumer.
Discover Mend SCA

“One of our most indicative KPIs is the amount of time for us to remediate vulnerabilities and also the amount of time developers spend fixing vulnerabilities in our code base, which has reduced significantly. We’re talking about at least 80% reduction in time.”


“When the product you sell is an application you develop, your teams need to be fast, secure and compliant. These three factors often work in opposite directions. Mend provides the opportunity to align these often competing factors, providing Vonage with an advantage in a very competitive marketplace.”


“The biggest value we get out of Mend is the fast feedback loop, which enables our developers to respond rapidly to any vulnerability or license issues. When a vulnerability or a license is disregarded or blocked, and there is a policy violation, they get the feedback directly.”


FAQs
How does Mend.io continuously update an SBOM?
Mend SCA rebuilds the inventory of open source libraries, packages, and third-party components on every scan, so the SBOM reflects the dependency tree in the repository today, not at the last audit. Teams can generate SBOM reports in SPDX and CycloneDX, choose library- or file-level detail, import third-party SBOMs, and keep everything current across every application.
Which SBOM formats and versions does Mend.io support?
Mend SCA exports SPDX 2.2 and 2.3 as JSON, XML, YAML, Excel, or tag-value, and CycloneDX 1.4, 1.5, and 1.6 as JSON or XML. CycloneDX exports embed VEX data. Every component includes a package URL (purl) for interoperability with other tools. CycloneDX 1.6 has semantic support.
How is Mend.io’s continuous inventory different from a static SBOM export?
A static export is outdated by the next commit. Mend SCA regenerates the inventory as dependencies change, so security reviews and audits run against your actual current risk.
New to SBOMs? Start with what an SBOM is and its key benefits.
How does Mend.io incorporate VEX into SBOMs?
Mend SCA embeds VEX data in CycloneDX exports. Each finding carries an analysis state: reachable findings are marked exploitable, findings with a Jira issue are marked in triage, and suppressed or unreachable findings are marked accordingly, so consumers of your SBOM can tell which vulnerabilities actually matter without re-triaging your work.
Can Mend.io SBOMs satisfy EO 14028 and EU Cyber Resilience Act requirements?
Yes. Mend.io SBOMs are machine-readable in the SPDX and CycloneDX formats those regulations reference, carry per-component identifiers and license data, and regenerate on every scan, which meets the transparency and currency expectations both set.
For the regulation itself, see our EU Cyber Resilience Act compliance guide.
How does Mend.io prioritize risks found in an SBOM?
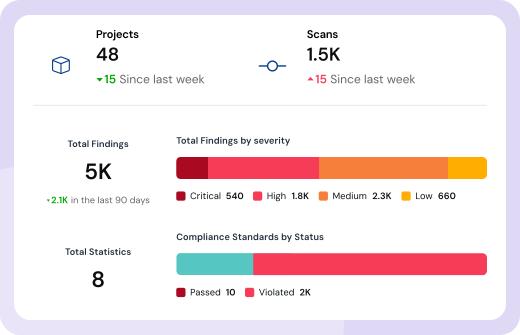
Mend SCA enriches the component inventory with vulnerability severity, reachability, exploitability signals, dependency paths, remediation guidance, and malicious-package status. Reachability analysis helps identify whether application code can reach a vulnerable component in supported environments, while additional risk factors help teams focus on vulnerabilities with stronger evidence of real-world risk.
How does Mend.io’s SBOM fit into existing build and CI/CD systems?
SBOMs come from the same Mend SCA scan that runs in your repository integration (GitHub, GitLab, Bitbucket, Azure DevOps) or from the Mend CLI in any CI/CD job, so no separate generator or pipeline step is needed. Reports can be generated per project or aggregated across an application, or downloaded from the Mend AppSec Platform.
Stop managing alerts.
Start reducing risk.
Join the teams reducing remediation effort by 75%.