Checkmarx SBOM
Ensure compliance, enhance security, and streamline your cybersecurity practices
with a comprehensive software bill of materials (SBOM) tool.
Elevate Your Compliance with Checkmarx SBOM Security
Designed to meet these compliance challenges head-on, our solution provides an automated and efficient way to generate and maintain SBOMs.
Automatic Generation
Our SBOM tool automates the creation of SBOMs, enabling you to effortlessly generate comprehensive inventories of your software components.

Easily Shareable
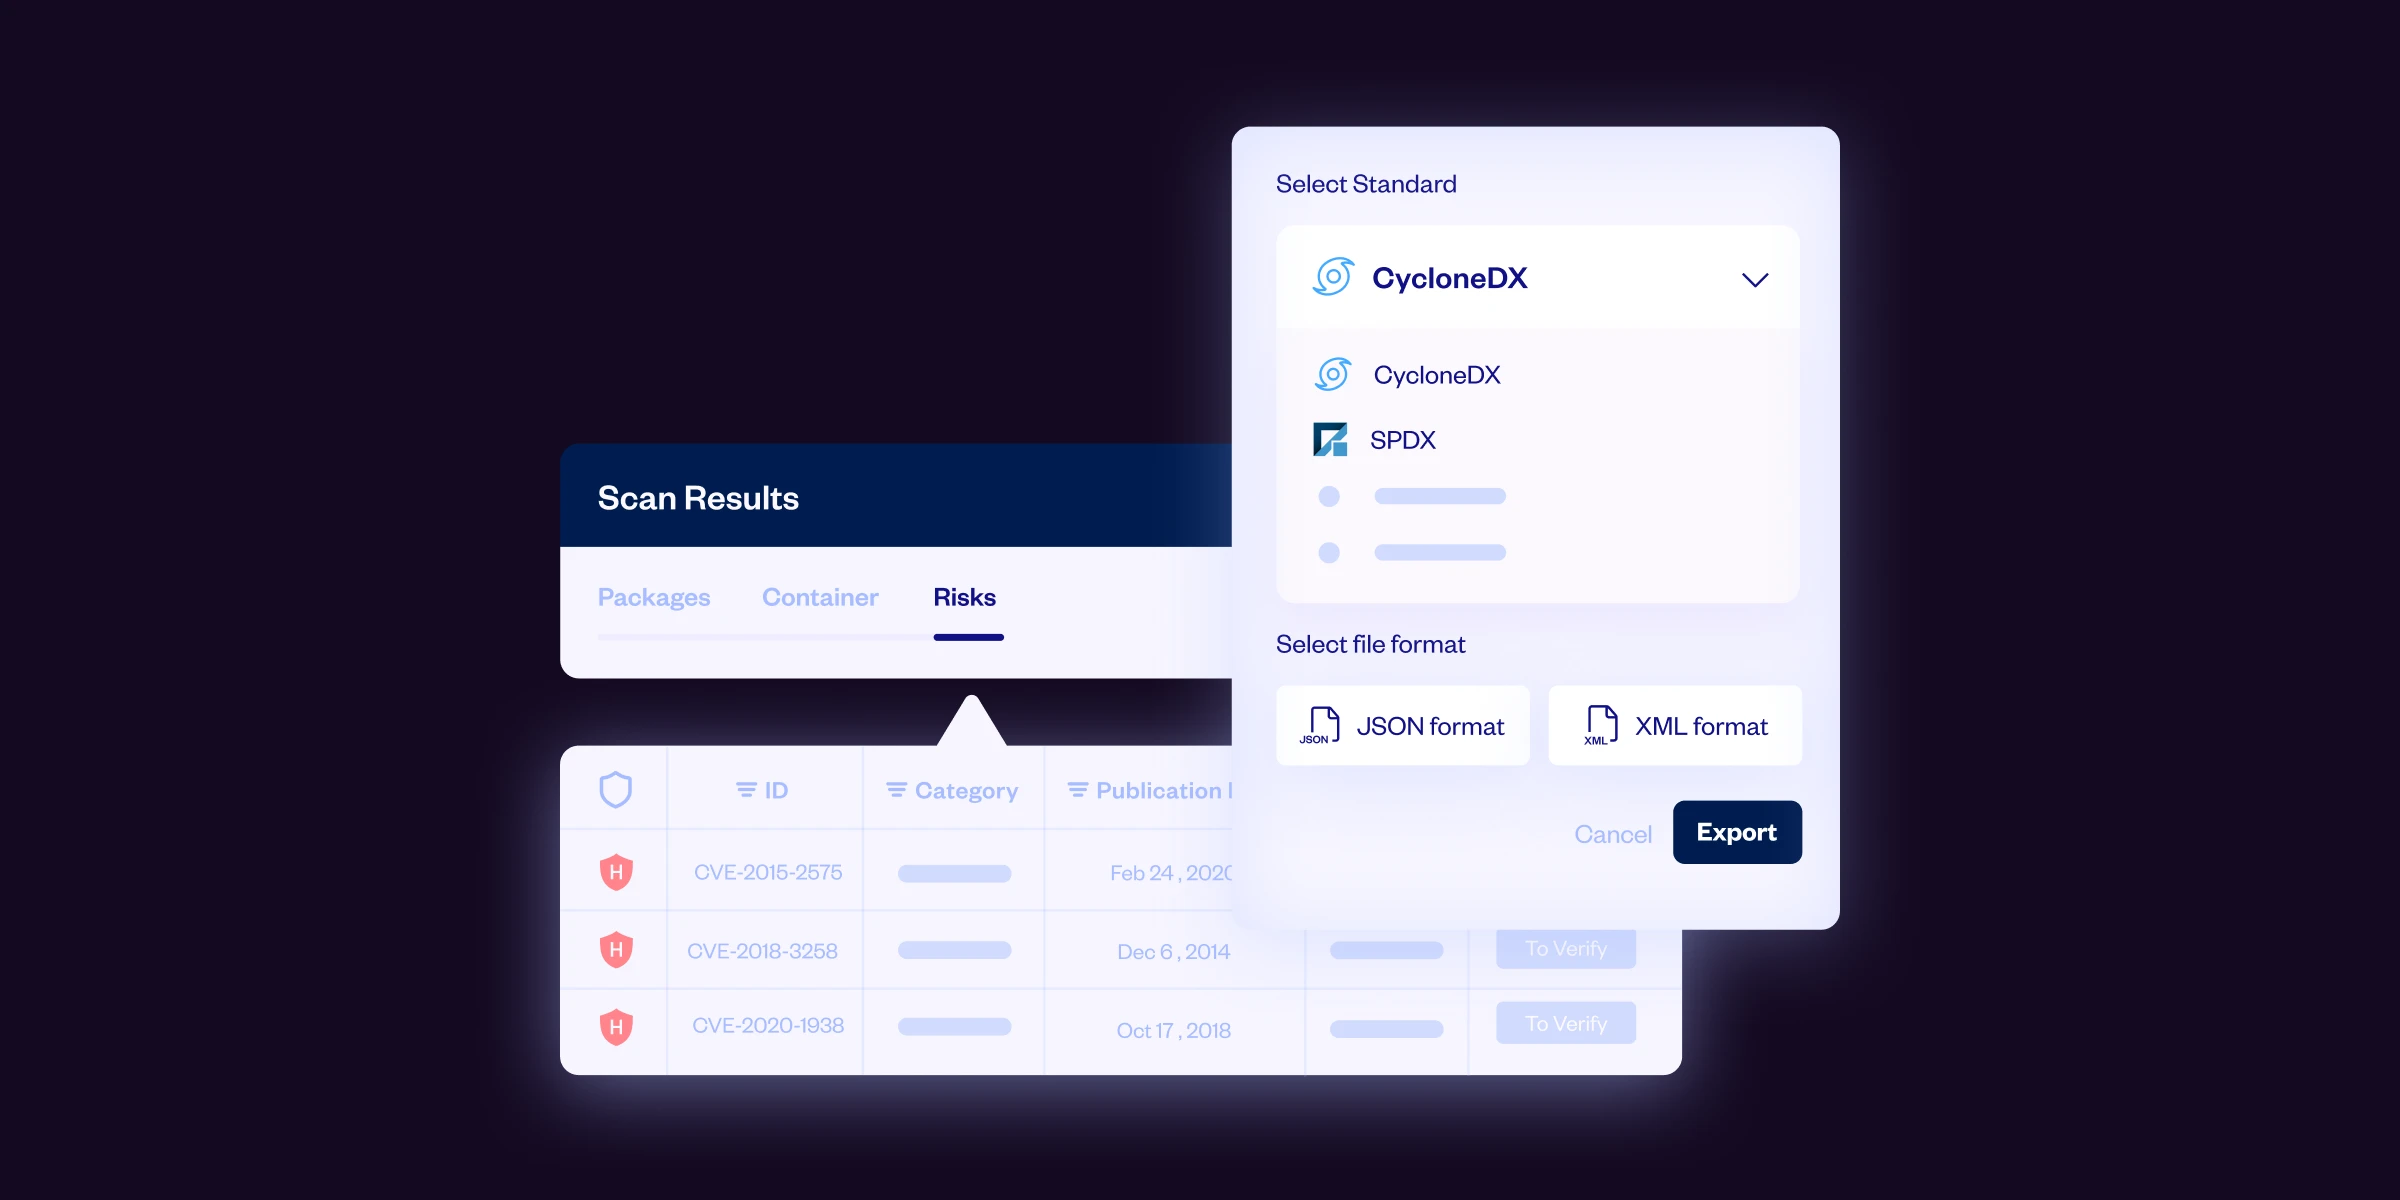
Export your SBOMs in standard formats — including SPDX and CycloneDX — with a single click.
Seamless SCM Integration
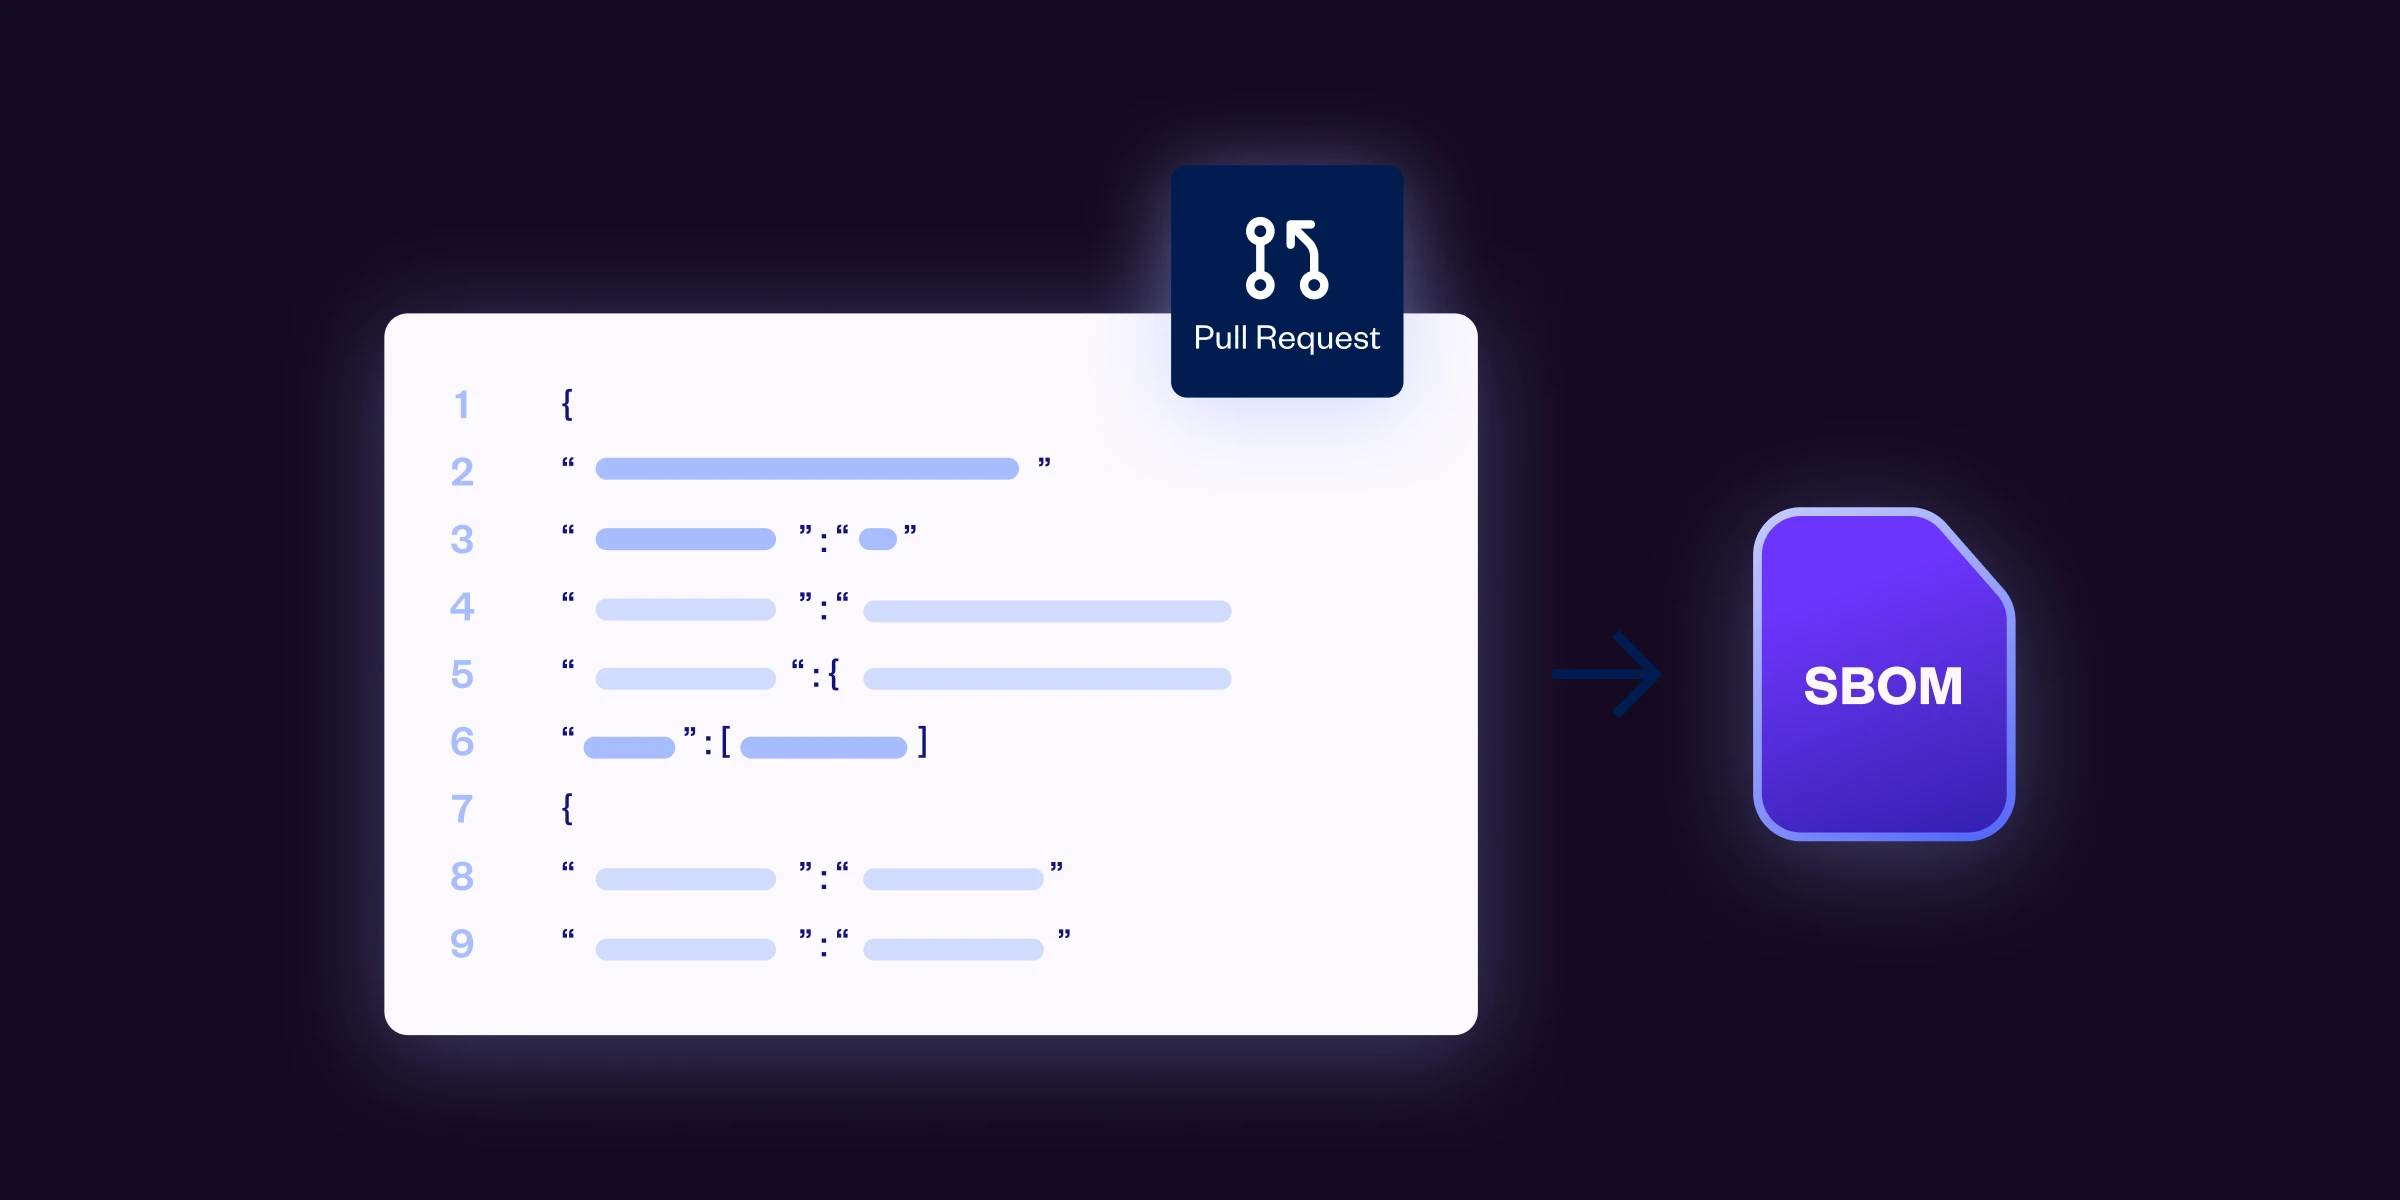
Integrates directly with your source code management (SCM) systems, automatically triggering scans and SBOM updates on every push and pull request so your SBOMs stay synchronized with the latest code changes.
Enhanced Third-Party SBOM Consumption
Import and enhance SBOMs from third parties, layering on Checkmarx’ detailed vulnerability insights for a deeper understanding of potential security risks.

Comprehensive Risk & License Analysis
Identify every open-source package in your SBOM and surface detailed risk and license findings from the Checkmarx Software Composition Analysis (SCA) database.

Historical SBOM Access
Access historical SBOMs from past scans or code checks without maintaining a separate catalog of files — so you are ready for compliance audits at any point in time.

The Checkmarx Approach
to SBOM
Automate, secure, and simplify your software inventory management for government-grade security standards.


How Organizations Benefit
from Checkmarx SBOM
Effortlessly navigate software component audits, streamline your compliance processes, and bolster your organization’s cybersecurity defenses.

Ensure Federal Compliance
Adhere to U.S. federal government mandates by providing complete, up-to-date SBOMs — making your software eligible for use within government agencies.

Save Time and Resources
Automate the generation and updating of SBOMs and reduce manual effort, so you can focus on what matters most — developing secure, high-quality software.

Historical Compliance and Readiness
Be prepared for any compliance check with access to a historical archive of SBOMs, ensuring transparency and accountability for past software versions.
Related Resources
 Report
Beyond SBOM: 2024 Trends: AI, Malicious Packages, and Everything In Between
Learn More
 Video
Discover How to Streamline Your SBOM Creation
Learn More
 Interactive Demo
Try It Yourself: Our Interactive Demo
Learn More
 Knowledge Hub
Understanding Software Bill Of Materials (SBOM)
Learn More
Why the World’s Top Teams Choose Checkmarx
“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”
“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”
“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
Frequently Asked Questions
An SBOM is a standardized, detailed inventory of all software components in a product. It includes information such as package names, versions, licenses, and dependency types — helping organizations identify and address vulnerabilities.
SBOM compliance is essential due to growing cybersecurity threats and government regulations. The U.S. federal government requires SBOMs for all software used within federal agencies to improve the nation’s cybersecurity.
Checkmarx SBOM automates the creation and updating of Software Bills of Materials, ensuring they are always current and comprehensive. This automation helps maintain compliance with U.S. federal mandates by providing a complete inventory of your software’s components and their security statuses.
Yes. Checkmarx SBOM allows for the consumption of third-party SBOMs, enhancing them with detailed vulnerability information and insights provided by Checkmarx for a more comprehensive security overview.
Checkmarx SBOM supports industry-standard formats such as SPDX (Software Package Data Exchange) and CycloneDX, facilitating easy integration and sharing with stakeholders and regulatory bodies.
Checkmarx SBOM integrates with your source code management (SCM) system, automatically triggering scans and updating SBOMs with every code commit, push, or pull request. This ensures that your SBOMs are always synchronized with the latest changes in your software.
Checkmarx SBOM maintains a historical record of all scans and SBOM generations. You can easily retrieve point-in-time SBOMs for any previous scan or code check, ensuring you have the documentation needed for compliance audits or historical reviews.
Yes. Checkmarx SBOM supports a wide range of programming languages and package managers, ensuring comprehensive and consistent SBOM management across various projects and technologies.
Talk to an Expert
Join the growing club of enterprises that rely on Checkmarx to streamline federal compliance and robust software security with ease and precision.
Thank You!
Your Custom Checkmarx Demo Request was Successfully Sent!
Get a Demo
See How Checkmarx SBOM Works Today
Automatic SBOM generation across every push and pull request.
Standard-format export to SPDX and CycloneDX in a single click.
Risk and license findings backed by Checkmarx SCA intelligence.
Historical SBOM archive for audit-ready compliance at any point in time.
Get Started With
Checkmarx SBOM
Join the growing group of enterprises that rely on Checkmarx SBOM.
